> For the complete documentation index, see [llms.txt](https://docs.bypassec.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.bypassec.com/the-platform/hacking-competitions/researchers/reporting-findings.md).
# Reporting Findings
## Introduction
After registering as a researcher on the platform, you will gain access to available competitions and can begin reporting your first vulnerabilities.
## Competition Types
At Bypassec, we offer two types of tournaments:
* **Public**: Accessible to all researchers.
* **Private**: Restricted to high-performing researchers selected by Bypassec.
To view available competitions, access the "**Competitions**" tab within the platform.
Each competition has its own testing policy and scope, which can be viewed by clicking on the competition.
{% hint style="warning" %}
It is **strictly prohibited** to conduct tests on assets that are not explicitly defined in the scope section, as described in the Terms and Conditions of the platform.
{% endhint %}
## Reporting Vulnerabilities
To report a vulnerability, fill in all available fields and describe the exploitation process in detail.
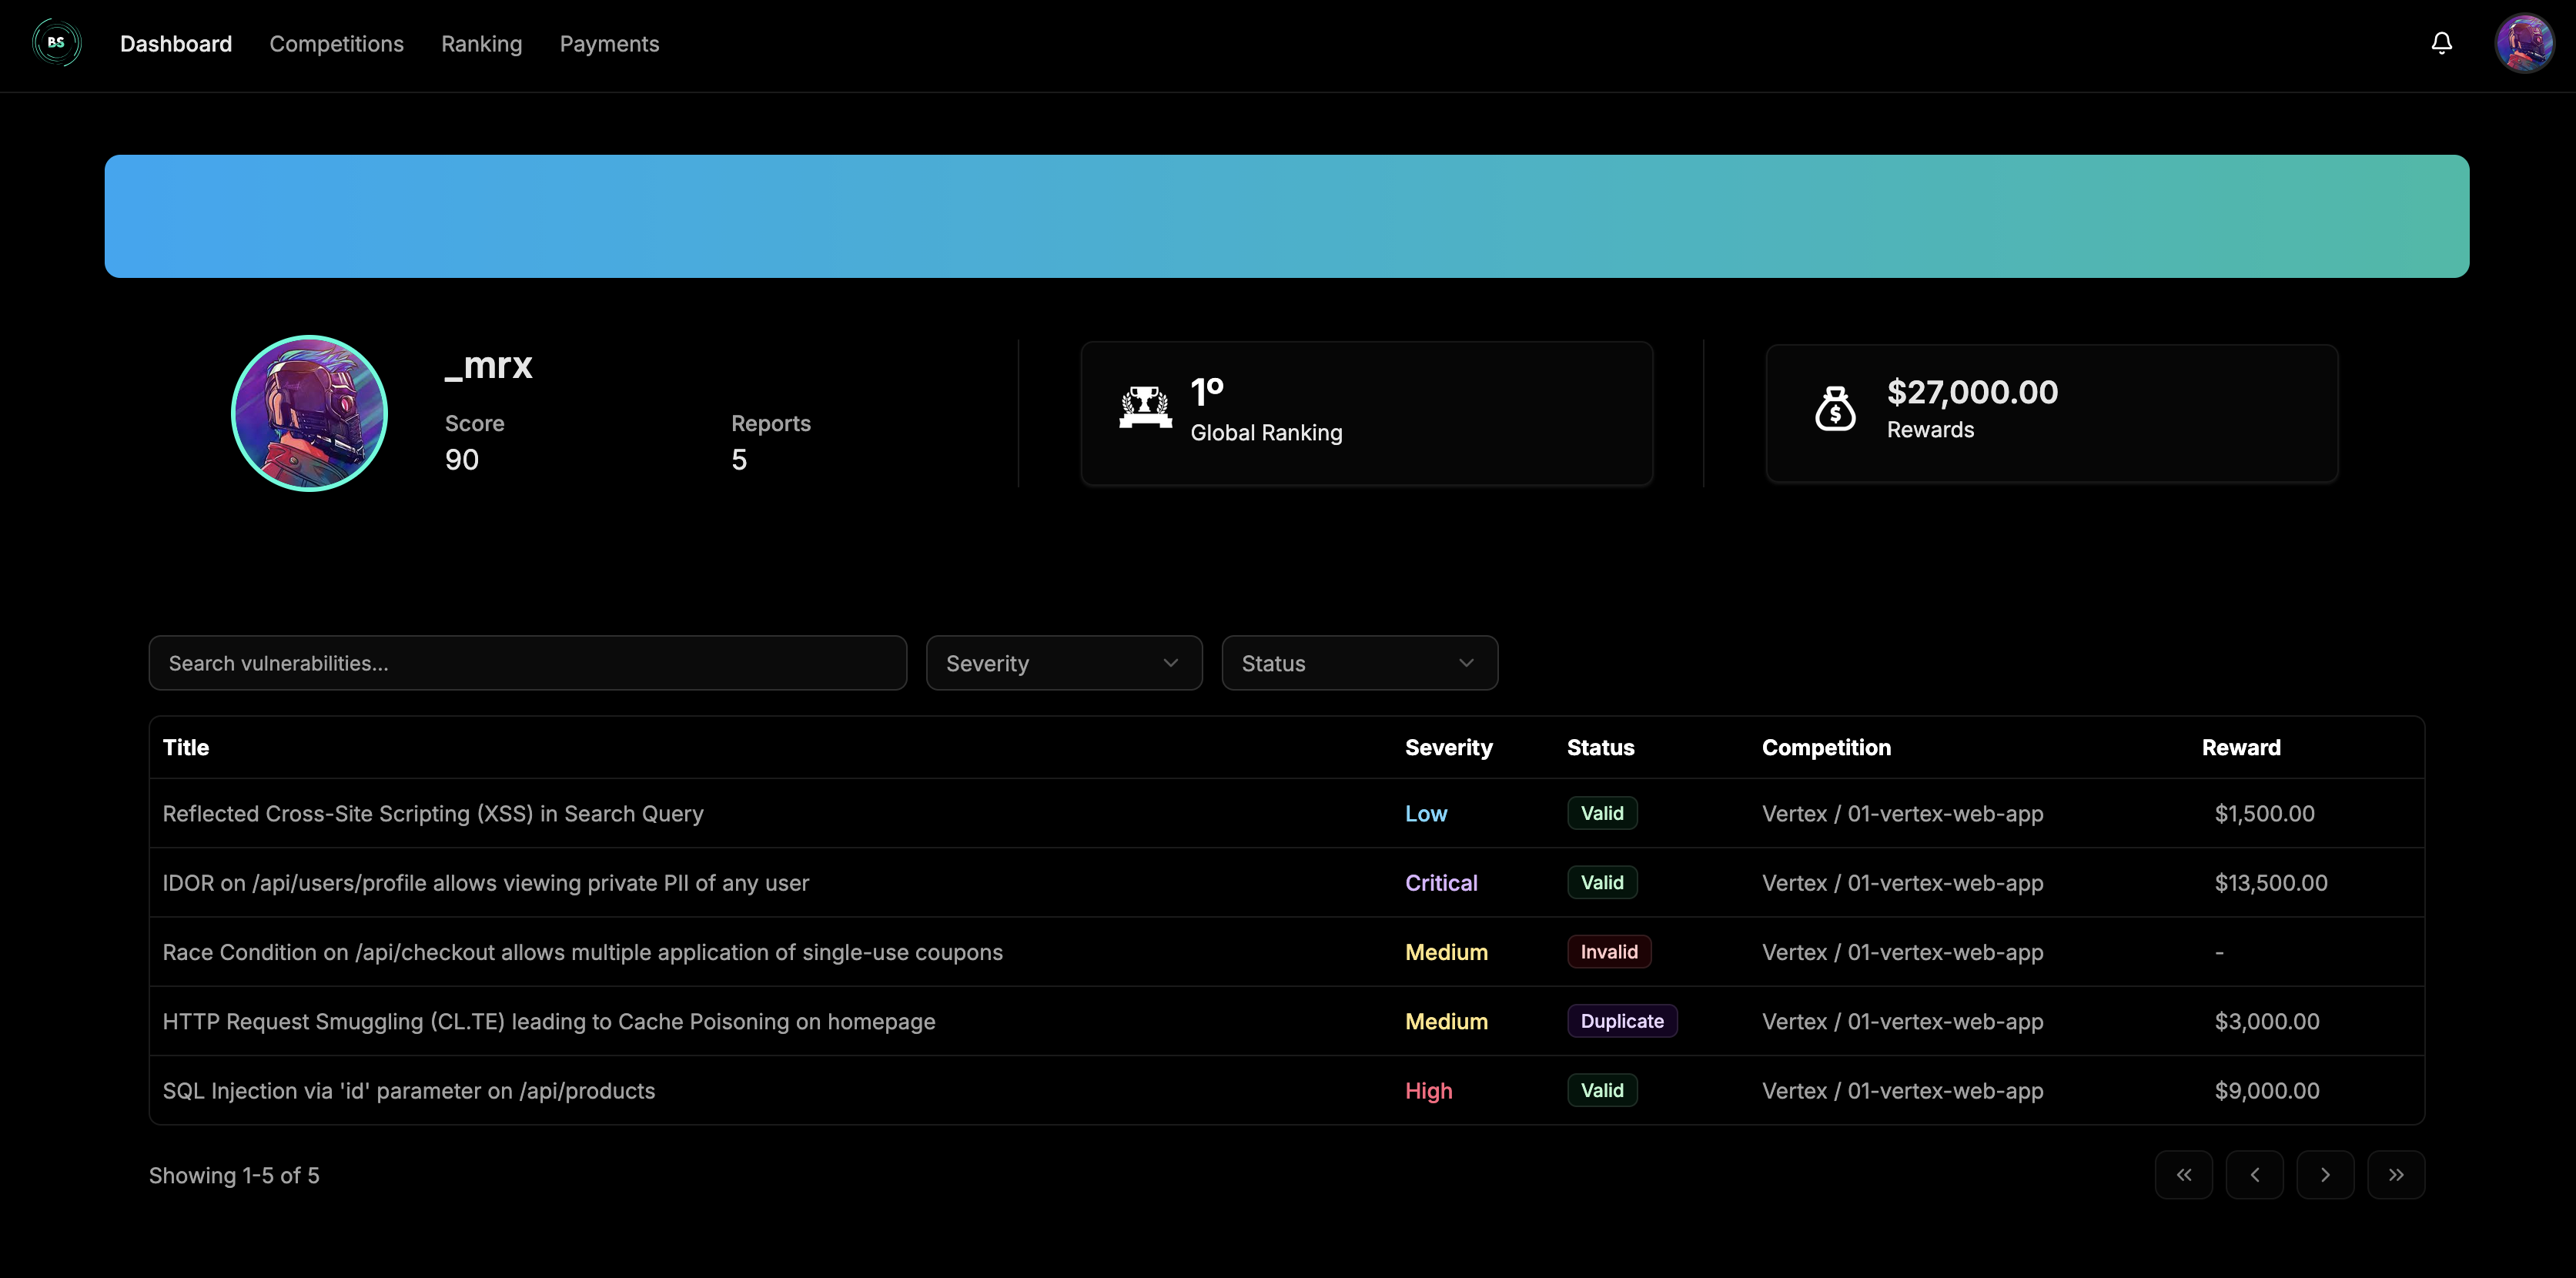
Once you have reported a vulnerability, you can track its progress in the "Dashboard" tab.
## Report Validation
When vulnerabilities are reported, they undergo a validation process by the Bypassec team before their status is updated.
Incomplete reports or those lacking a clear description and reproduction steps will be automatically invalidated and will not be eligible for a reward. Similarly, vulnerabilities that do not demonstrate a relevant impact on the organization will be considered invalid.
{% hint style="info" %}
Reports are validated only after the tournament has concluded.
{% endhint %}
The available statuses are:
* **Pending:** The vulnerability has been reported and will be validated by Bypassec at the end of the competition.
* **Duplicate:** The vulnerability is valid and has also been reported by other researchers.
* **Valid:** The vulnerability is valid and unique.
* **Invalid:** The vulnerability is invalid and will not be eligible for rewards.
{% hint style="warning" %}
During the validation process, Bypassec may contact the researcher via email or Discord if the report requires additional information. The researcher will have **48 hours** to respond before the vulnerability is invalidated.
{% endhint %}
## File Uploads
All evidence regarding the reported vulnerability must be submitted through the platform's native upload feature.
{% hint style="danger" %}
It is **strictly prohibited** to store or submit evidence using applications that make them publicly available without any protection or credentials.
{% endhint %}